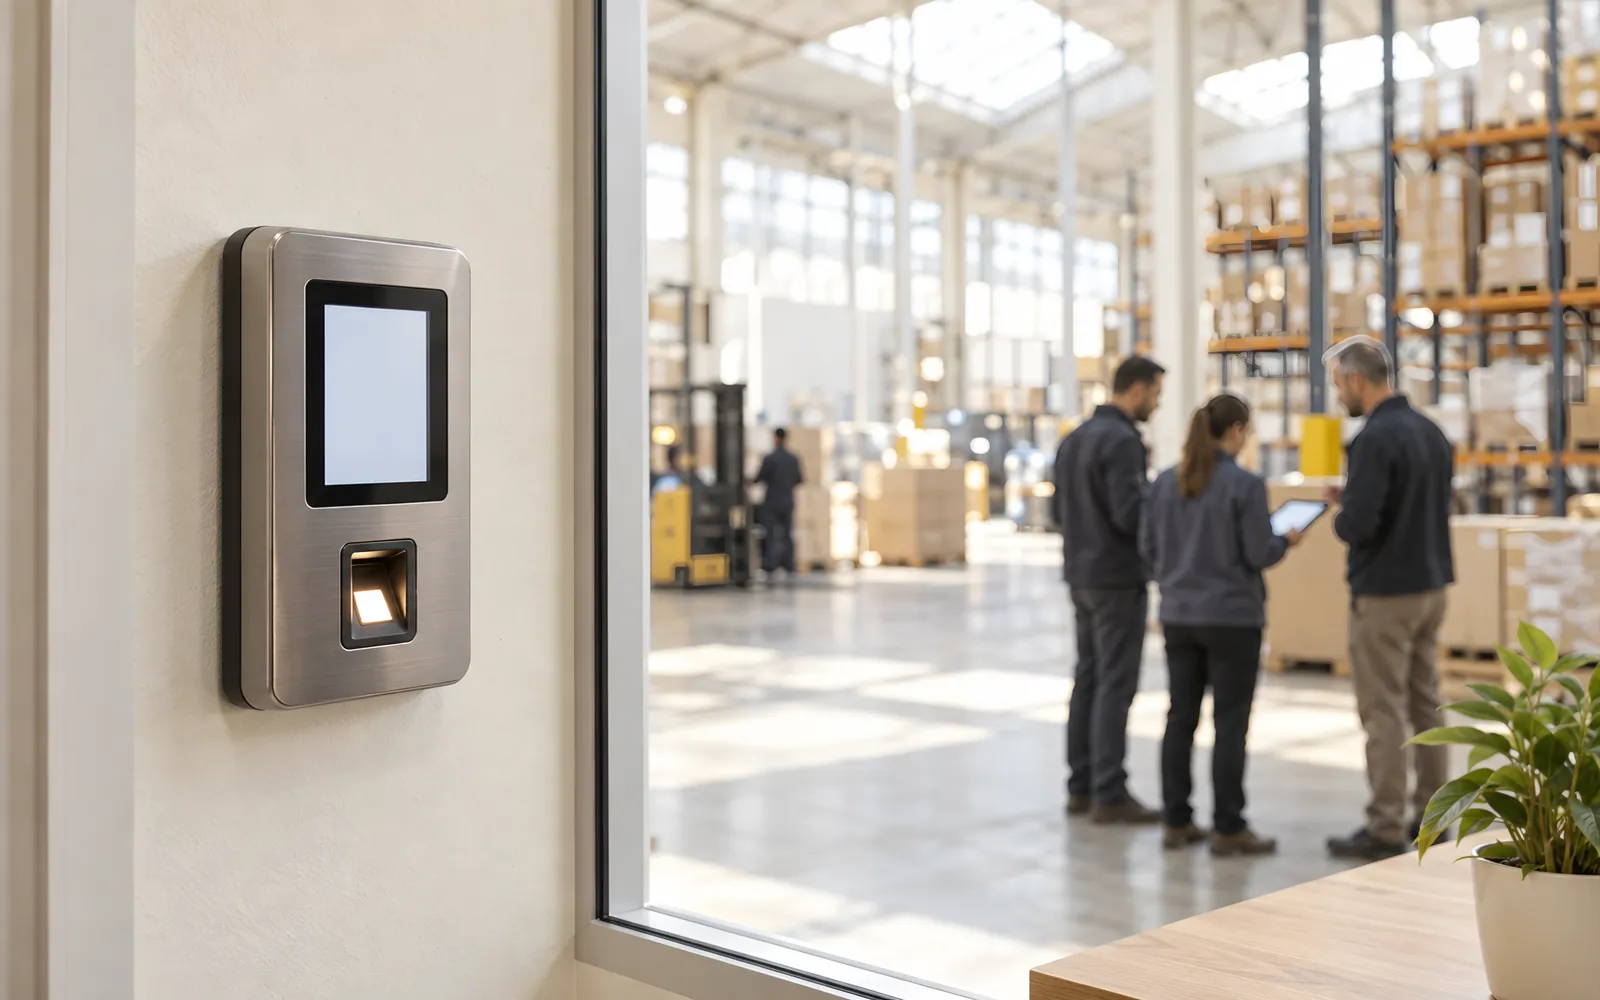
If your employees clock in with a fingerprint, a hand scan or their face, you are collecting biometric data, and in Illinois that brings you within the Biometric Information Privacy Act. BIPA was passed in 2008 and runs to only a few pages. It is also the reason Illinois employers have paid some of the largest privacy settlements in the country, because it gives individuals a private right to sue and sets damages per violation.
What the Act requires
In summary, a private employer that collects biometric identifiers or biometric information must:
- Have a written policy, available to the public, with a retention schedule and guidelines for permanently destroying the data.
- Destroy the data when the purpose for collecting it has been satisfied, or within three years of the person’s last interaction with the company, whichever comes first.
- Tell each person in writing, before collection, that their biometric data is being collected or stored, for what purpose, and for how long.
- Obtain a written release from each person before collection.
- Not sell, lease, trade or otherwise profit from the data, and not disclose it to anyone else without consent or another exception in the Act.
- Store and protect the data with at least the care it uses for other confidential and sensitive information.
Why the risk is so large
Anyone aggrieved by a violation may sue for liquidated damages of $1,000 for each negligent violation, or $5,000 for each intentional or reckless one, plus attorney’s fees and costs. The Illinois Supreme Court has held that a person does not need to show actual harm to sue, that a five-year limitations period applies and, in 2023, that a separate claim accrues each time a biometric is scanned or transmitted without the required consent. For a workforce clocking in and out twice a day, the theoretical exposure ran into the billions.
BIPA compliance is mostly paperwork. It just has to exist before the first scan, not after the first lawsuit.
What changed in 2024
In August 2024 the legislature amended the Act. When the same company collects the same biometric from the same person by the same method, that now counts as a single violation however many times the scan is repeated, so a person can recover only once. The amendment also confirmed that an electronic signature satisfies the written-release requirement.
The amendment limits exposure; it does not change the obligations. Statutory damages of $1,000 or $5,000 per employee, multiplied across a workforce and a five-year look-back, are still significant. Whether the amendment applies to claims that arose before it took effect has itself been litigated, so employers with older gaps in compliance should take advice on their own position.
The checklist
For an employer using biometric timeclocks, compliance comes down to a short list of tasks that most companies can finish in a few weeks:
- Inventory every device and system that touches biometrics: timeclocks, door access, phone apps and the vendor-hosted software behind them.
- Publish a written retention and destruction policy on your website and in the employee handbook.
- Collect a signed consent and release from every current employee before their next scan, and build it into onboarding so new hires sign before their first.
- Put the destruction rule into practice: a process, owned by a named person, that deletes templates when employees leave.
- Review the vendor contract. The vendor may itself collect or store the data, so the consent should cover it, and the contract should address security, deletion and indemnity.
- Offer a non-biometric alternative, such as a badge or PIN, for employees who decline. The Act does not require one, but it takes pressure off the consent.
- Keep the records: signed releases, the published policy and destruction logs.
Who is outside the Act
BIPA does not reach everyone. It excludes, among others, financial institutions subject to federal financial privacy law, information captured from patients in a health care setting, and government contractors working for a state agency or local government. The Illinois Supreme Court has also held that claims by unionized employees can be preempted by federal labor law where a collective bargaining agreement covers the subject. These exceptions turn on specific facts, so it is usually safer to comply than to rely on one.
Where to start
If you have never looked at BIPA, start with the inventory and the vendor contract, because together they tell you how large the job is. If you have a policy but no signed releases, collect them now. If you have received a demand letter, do not delete data or change your systems until you have spoken to counsel: how you respond in the first weeks can matter as much as what happened before.